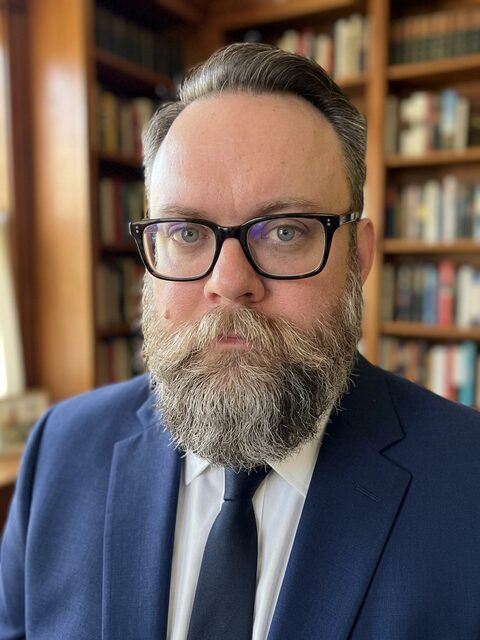
The full history: roles, employers, and dates, authored from the same public PDF you can download. Twenty-plus years in enterprise IT, from bench technician to senior IT infrastructure engineer.
IT Engineer | Cloud, Infrastructure & Automation | St. Louis, MO
Marcus
Whitman
I administer cloud, Microsoft 365, and identity infrastructure for a managed services provider serving 44 client organizations, 21 of them on Microsoft 365, and build the PowerShell and Python tooling that keeps it documented, audited, and repeatable. Recent work includes a 3,500-document migration out of SharePoint, a standing security audit program, and delegated administration that replaced per-client admin accounts with a single secured identity per technician.
work
Selected infrastructure and automation work, written up as case studies. Employers are named; clients are described by sector only, with identifying details removed.
SharePoint-to-IT-Glue Migration
Roughly 3,500 documents across 28 organizations moved out of SharePoint via the Microsoft Graph API, checkpointed and resumable end to end.
Multi-Tenant Delegated Administration
Per-client admin accounts replaced with one secured identity per technician across every managed tenant: CSP/GDAP role design, consent at scale, and automation that works under delegation.
Security & Infrastructure Audit Program
A standing audit program across 44 client organizations that caught what spot checks missed, including expired perimeter security licensing that had left threat protection off, tracked to closure on a fixed cadence.
Phishing-Simulation Platform
SaaS subscription costs traded for a self-hosted simulation stack on Azure that has delivered multiple paid awareness engagements: scripted Azure CLI configuration, TLS, SMTP relay, and secrets in Key Vault.
RMM-to-Documentation Pipeline
Per-site network documentation generated from live RMM inventory instead of maintained by hand: gateway-first site detection over the NinjaOne API, written into IT Glue on demand.
the demo
AI wrote the script. The standards were mine.
In 2019 I wrote the kind of provisioning script every shop had: hardcoded paths, a plaintext password, six hand-edited copies. In 2026 I rebuilt the same task for Microsoft Entra by directing an AI with a crafted prompt and codified PowerShell standards. Both scripts are public, and the gap between them is what the demo demonstrates.
The walkthrough shows the 2019 script annotated line by line, the exact prompt and standards that directed the rebuild, eight design decisions with the reasoning written out, and a replay of the new script's dry run. The dry run needs no tenant and no Graph module, so you can reproduce it yourself.
pwsh - offline dry run (-WhatIf)
PS C:\entra-provisioning-demo> pwsh -File src/New-EntraUsersFromCsv.ps1 -CsvPath data/new-hires.csv -WhatIf
[2026-07-08 00:08:49] [INFO] Read 9 rows from data/new-hires.csv.
[2026-07-08 00:08:49] [WARNING] Row 8: SKIPPED (missing field(s): First).
[2026-07-08 00:08:50] [INFO] PLAN Jamie Doe: create jdoe2@contoso.com | group Legal-Support-Users | license SPE_E3 (group-based) | TAP valid 2026-07-13 -> email alan.pierce@contoso.com
What if: Performing the operation "Create Entra user, add to 'Legal-Support-Users', issue Temporary Access Pass, email manager" on target "jdoe2@contoso.com".
jdoe2 is the collision handler at work: there is already
a jdoe in the same batch. The full replay, including the skipped
rows and the seven-row summary, is in the walkthrough. Demo identities and
domains are fictional.